Autonomous detection ​without tradeoffs.

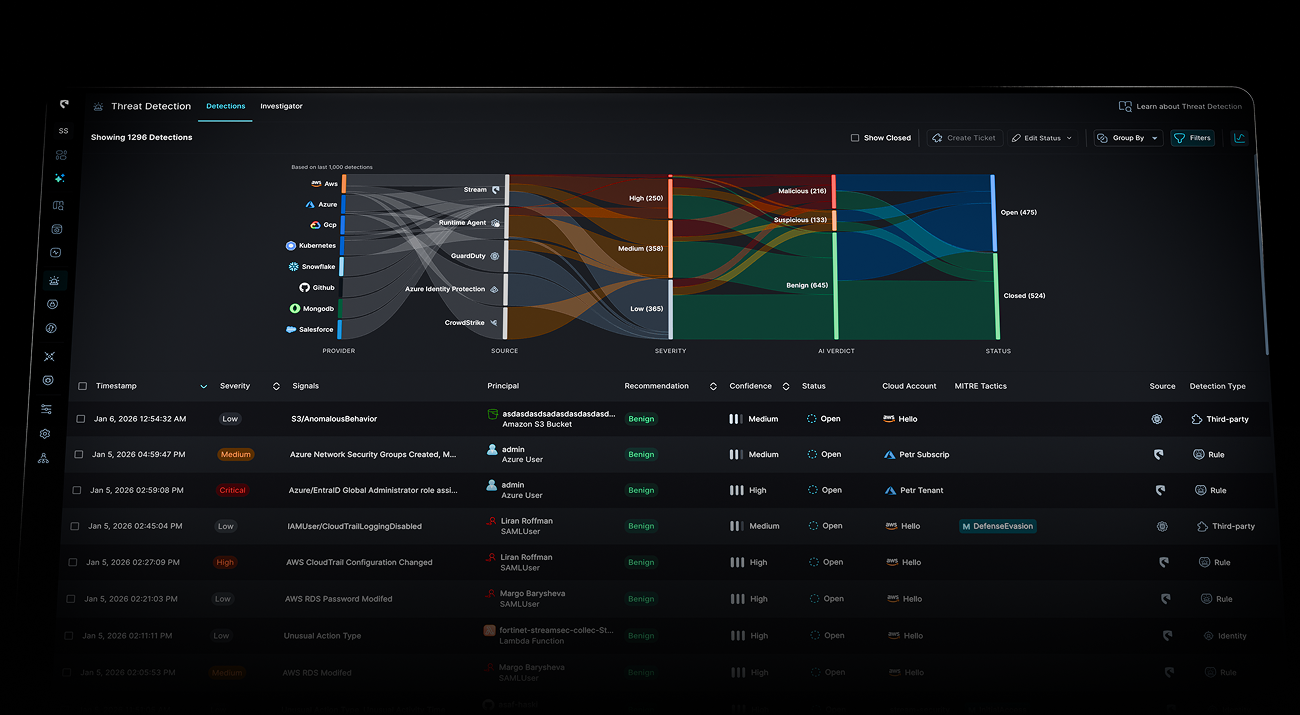
Detects and triages attacks across every boundary

Raw telemetry flattens everything into noise. ProductionTwin gives every detection its real exploitability, reachability, and blast radius - ready to close, not just flag.
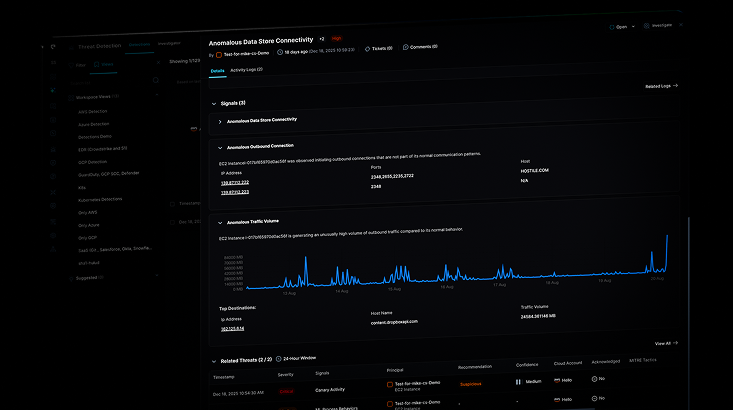
Threat Detection showing Anomalous Data Store Connectivity with details on outbound connections, traffic volume graph from August 13-20, and related threat activity including severity and confidence levels.

Complete detection coverage out of the box

A layered detection model at log-ingest speed

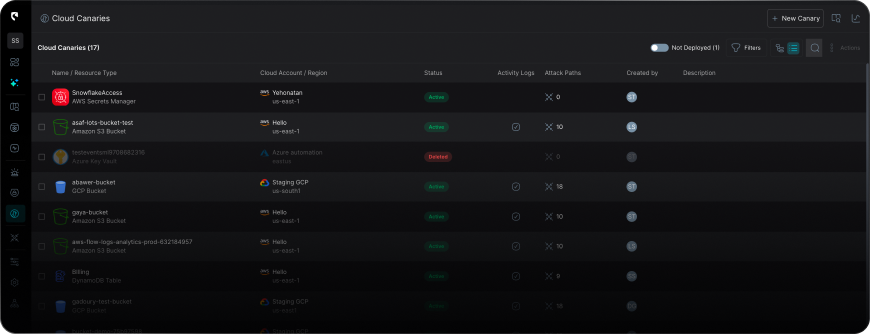
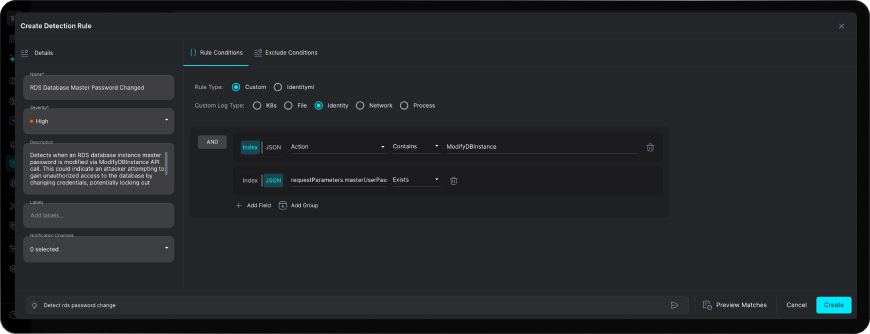
Stream combines rules, stateful behavior analytics,​ IOCs and canaries, covering Audit logs and eBPF sourced data.
You can also bring your existing detection signals​ into the model from EDRs and any other source you have.
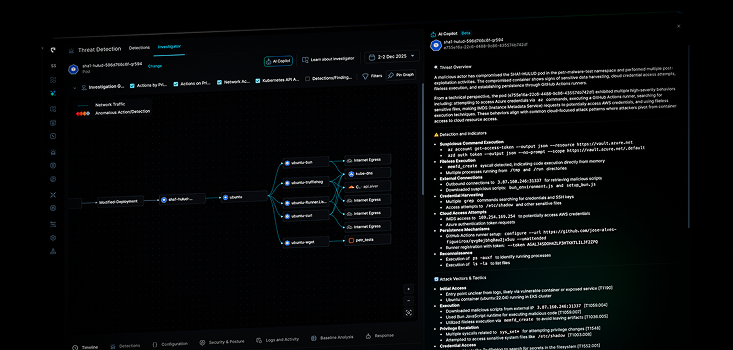
User interface of a Threat Detection Investigator showing a flow diagram of a compromised pod, detailed threat overview, detection indicators, and a timeline of triggered detection rules.

eBPF runtime threat detection

Detect exploits at the application layer, stop them before they spread.

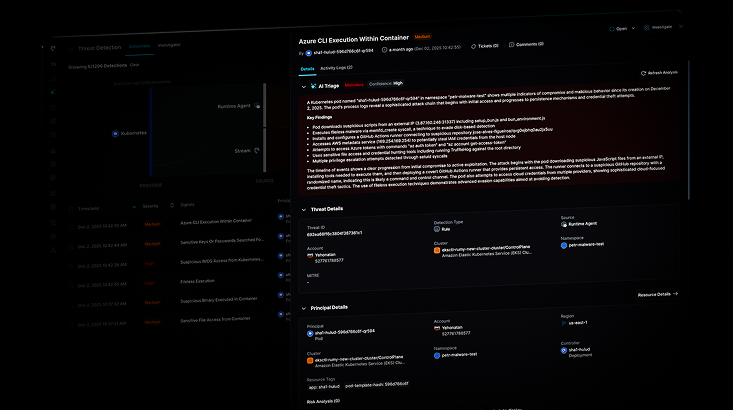
Detect threats using eBPF sourced telemetry accross Network, API, File and Process activity.
Block known patterns, respond with AI when needed.

Understand the Potential Impact Instantly
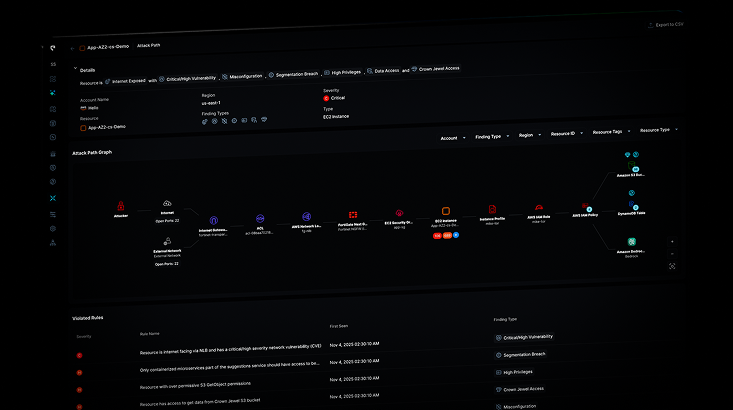
Real-time exploitability potential and blast radius are automatically considered to prioritize every detection severity

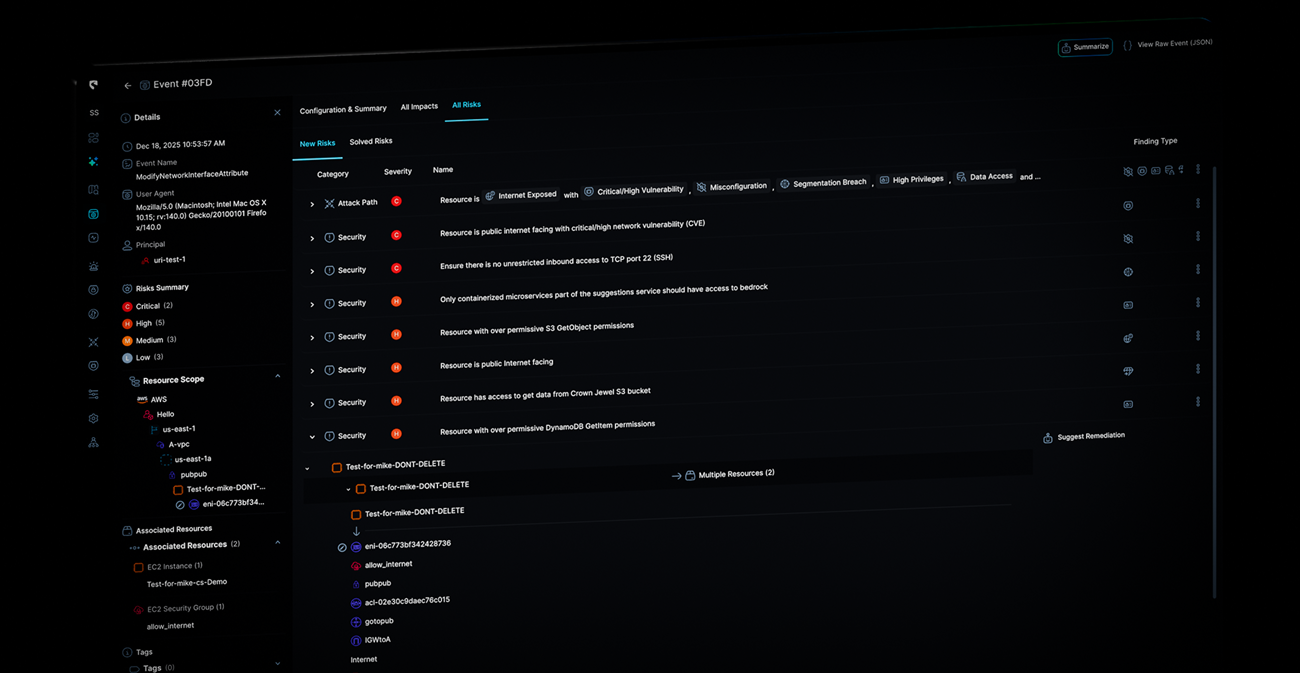
Every alert is enriched with real-time cloud context to instantly calculate risk and blast radius. Stream shows exactly what’s exposed and what can happen next.
Threat Detection dashboard showing details and risk analysis of an anomalous AWS EC2 instance connectivity with high severity alerts and unusual outbound connections.

Raw telemetry flattens everything, so traditional tools can’t tell noise from real risk. ​

We wouldn’t believe it either.

Get a demo

What's new