Stream CDRGoat: Real World Attack Simulations for Threat Detection Readiness
Stream's CDRGoat is an open-source project that lets SecOps teams safely validate detections and investigations against realistic cloud attack paths. Each scenario, developed by Stream’s Security Research and Product teams, includes vulnerable infrastructure and walks through a guided live attack to show exactly how adversaries exploit cloud environments in practice.
Stream's CDRGoat is an open-source project that lets SecOps teams safely validate detections and investigations against realistic cloud attack paths.
Each scenario, developed by Stream’s Security Research and Product teams, includes vulnerable infrastructure and walks through a guided live attack to show exactly how adversaries exploit cloud environments in practice.
Cloud adoption has changed how attackers operate. Today’s most successful breaches are carried out by cloud conscious attackerswho manipulate the configuration layer to improve their foothold, allowing them to carry out extensive attacks undetected.
That’s why we built CDRGoat: to help SecOps validate how their tools and teams respond to realistic cloud-native attack paths while remaining safe and isolated.
Ready to dive deeper? Explore CDRGoat and walk through a realistic attack scenario.
Stream CDRGoat - Scenario 1
What is Stream’s Cloud Detection and Response (CDR) Goat?
CDRGoat is a scenario-driven project focused on cloud-native advanced attack simulations, where manipulated configurations and weaknesses are combined with live attack techniques to demonstrate how adversaries exploit them in practice.
Advanced simulations - Scenarios fuse together posture issues, like excessive permissions or exposed services, with active attacker behaviors such as privilege escalation, credential theft, or lateral movement.
Detection and response validation - Each scenario is designed so defenders can confirm whether alerts fire, understand the context of the signal, and practice investigation workflows.
Safe by design - All activities run in isolated cloud environments, deployed and destroyed with Terraform, ensuring no risk to production workloads.
Deploy Scenario 1 and validate your detections against the attack scenario.
CDRGoat includes scenario packages that contain:
Attack overview and diagrams.
Terraform scripts that provides the vulnerable infrastructure on which the attacks run.
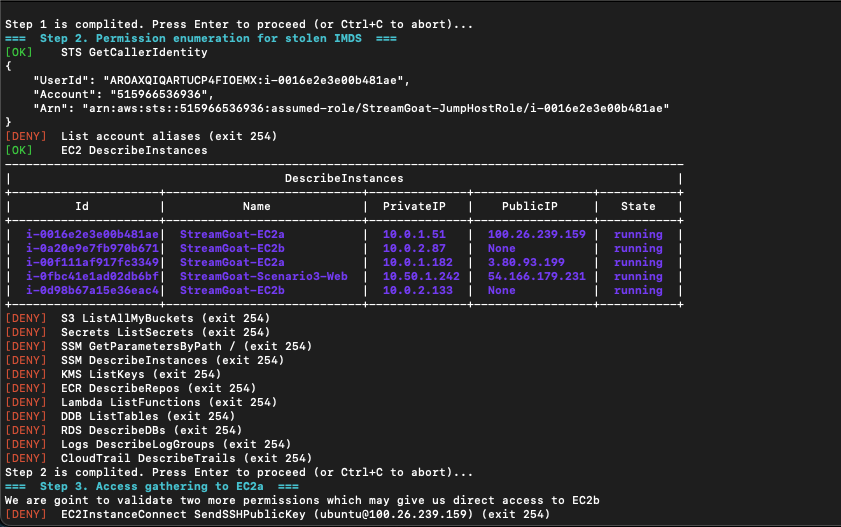
Automated attack scenarios with inline, step-by-step guidance.
Teardown instructions to remove the vulnerable environment.
CDRGoat’s Guided Attack Scenario Steps
Why SecOps Teams Need CDRGoat
CDRGoat helps SecOps teams spot multi-stage cloud attacks, connect signals across diverse log sources, and see how configuration changes (which may seem benign) can escalate into serious incidents. The result is stronger detections, faster investigations, and greater confidence that when an alert fires, teams know exactly what it means and how to respond.
*While the current scenarios focus on common AWS attack paths, the CDRGoat project will continue to expand to address a broader range of environments and threat models.
Disclaimer
This content is provided for educational and informational purposes only. Stream.Security’s CDRGoat is provided as-is without warranties of any kind. By using this project you accept full responsibility for all outcomes. Scenarios are intentionally vulnerable and must only be deployed in isolated, non-production accounts. Stream.Security does not guarantee the accuracy or completeness of the content and assumes no liability for any damages resulting from its use.
Stream.Security does not endorse or condone any illegal activity and disclaims any liability arising from misuse of the material. Stream.Security and project contributors assume no liability for misconfiguration or unintended consequences, including any illegal activity. Ensuring safe and appropriate use is your responsibility.
AboutStreamSecurity
Stream is the AI-native platform built to fight AI-enabled attacks. It autonomously prevents, detects, hunts, and remediates exposures and threats across production at machine speed - driving risk toward zero. It replaces the fragmented stack of scanners, runtime agents, exposure tools and playbooks with one live model of production.Defending Production needs a new approach: Stream is the only Autonomous Production Defense Platform that works across your entire production estate. It runs on a patented CloudTwin®, a high-fidelity security data harmonization layer that models Cloud, SaaS, identity, runtime, AI, network, perimeter, on-prem, security controls, and the behavior running on top of them into one live model of production: real-time, fully correlated, continuously updating. Not a snapshot. And it does not stop at boundaries - the boundaries that fragment every other tool are the same boundaries an attacker moves across. Inside CloudTwin they are one system.